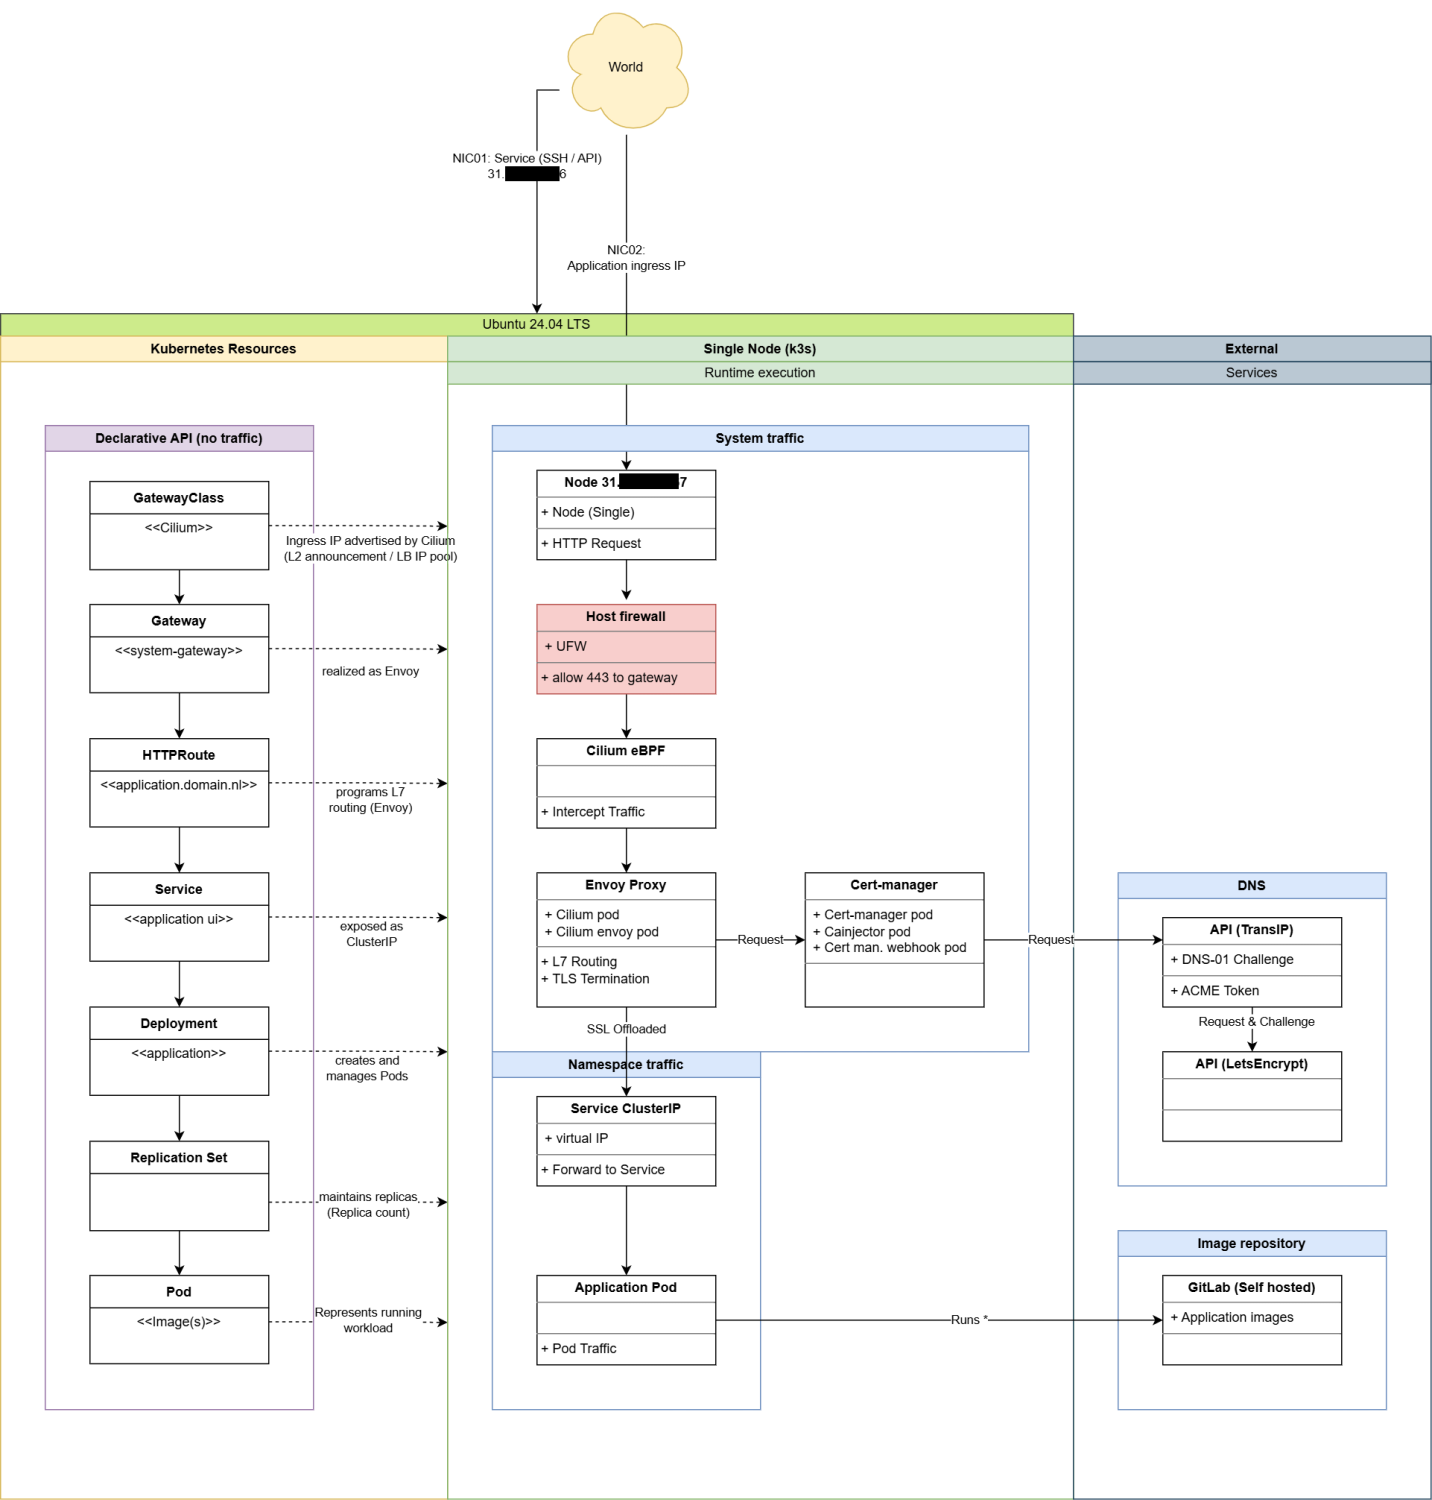
Following up on my previous article about Kubernetes, I deliberately sat down to draw out the network flow and deployment of my setup. This is how I think I built it and how I think it runs. That does not automatically mean it actually works exactly like this; it is my current mental image of the system.
In the image I show how, in my understanding, traffic travels from the outside world via DNS, Gateway API and Cilium eBPF to an application pod. Including TLS termination, cert-manager, Envoy, ClusterIP services and the difference between what you describe declaratively in Kubernetes and what actually happens at runtime on a single node k3s cluster. I also included host firewall rules and image delivery via GitLab.
The goal is simple: getting clear for myself what happens, where things start and end, and which assumptions I am making. By drawing it out you quickly notice where you hesitate or where your knowledge is thinner than you thought. That helps with debugging, security decisions and next steps.
If you read this and think: this is wrong, this could be sharper, or this works differently, I would love to hear it. Feedback from people with more or different Kubernetes experience is welcome. I am just getting started ;-)